Internet in the houses
Basics on LAN, WLAN and speed.
Many rooms have wired LAN. If wired LAN is available, this is the fastest and best way to use the internet. In these rooms and apartments we do not guarantee WLAN reception.
In ALMOST all rooms there is WLAN via the networks SMUC (encrypted, password 'akademiker') or unencrypted via STUDENTENWOHNHEIME-MUC.
LAN cable is always best. Next best is 5 GHz WLAN according to the AC standard. All access points of this standard have 5AC in the name (e.g. STUDENT_CAP_5AC) and are fast. Also good is the 5 GHz range named STUDENT_CAP5. Poor is the 2 GHz range – because it is very crowded. It is named STUDENTENWOHNHEIME-MUC or STUDENT_CAP, depending on the device model.
That means: STUDENTENWOHNHEIME-MUC
or STUDENT_CAP are great because they are available throughout all houses – e.g. for the smartphone.
Much faster, however, are the 5 GHz access points, which do not allow roaming and therefore have different names at every location in the building.
Usage and speed
We measure your volume used over the last 15 days every day. Fastest – unlimited and highest priority – are those
who were below the average of all users in that period.
Slowest are those who use more than 17 times the 15-day average of all students.
That is almost impossible with legal use. File sharing is illegal in Germany – and will quickly put you in the slowest category.
In between there are 3 further priority steps. The fastest of the current 8 steps is currently 4 Mbit upload, 40 MBit download with short-term peak 10M/120M.
The "slowest" is 2.5M/18M with peak 4M/70M. For normal internet use including Microsoft Teams and other video-chat apps, even the slowest step is enough.
The main difference is that the slowest have lower priority than the light users. That is not so bad, because light users
hardly use the internet anyway – so there is enough spare capacity.
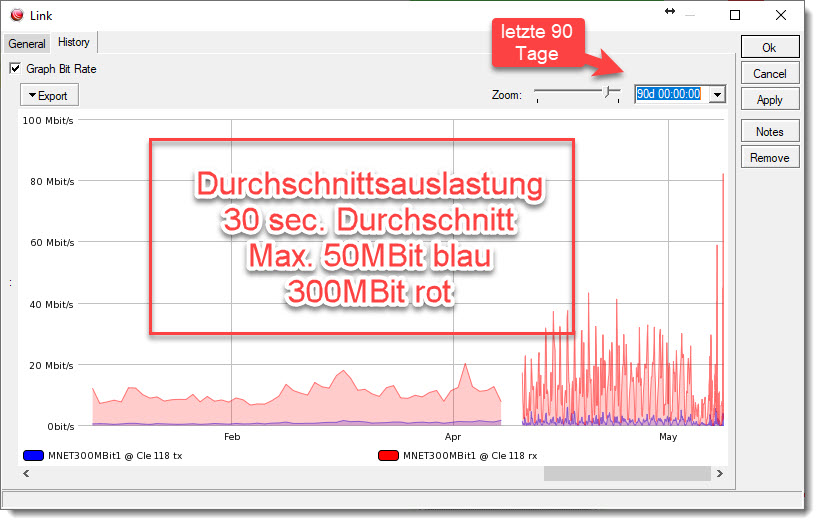
As you can see, our lines are far from fully loaded on average. The load is spread across several lines.
At Clemensstr. 118 as of 2023, for example, 2 MNet fibre lines with 1000 MBit each and 2 Telekom lines with 250 MBit each are active.
Several computers / phones / tablets
Currently 5 devices per user are allowed.
1 fast device (usually laptop or router) – logs in with VPN????@STUDENT as username.
4 slower devices (tablet, phone) log in with VPN????@PHONE (800k/15M with peak 5M/60M), usually on WLAN.
WLAN, cable:
Internet is now available in all apartments of the houses Clemensstr. 118,
Emanuelstrasse and Gabelsbergerstrasse via LAN (cable).
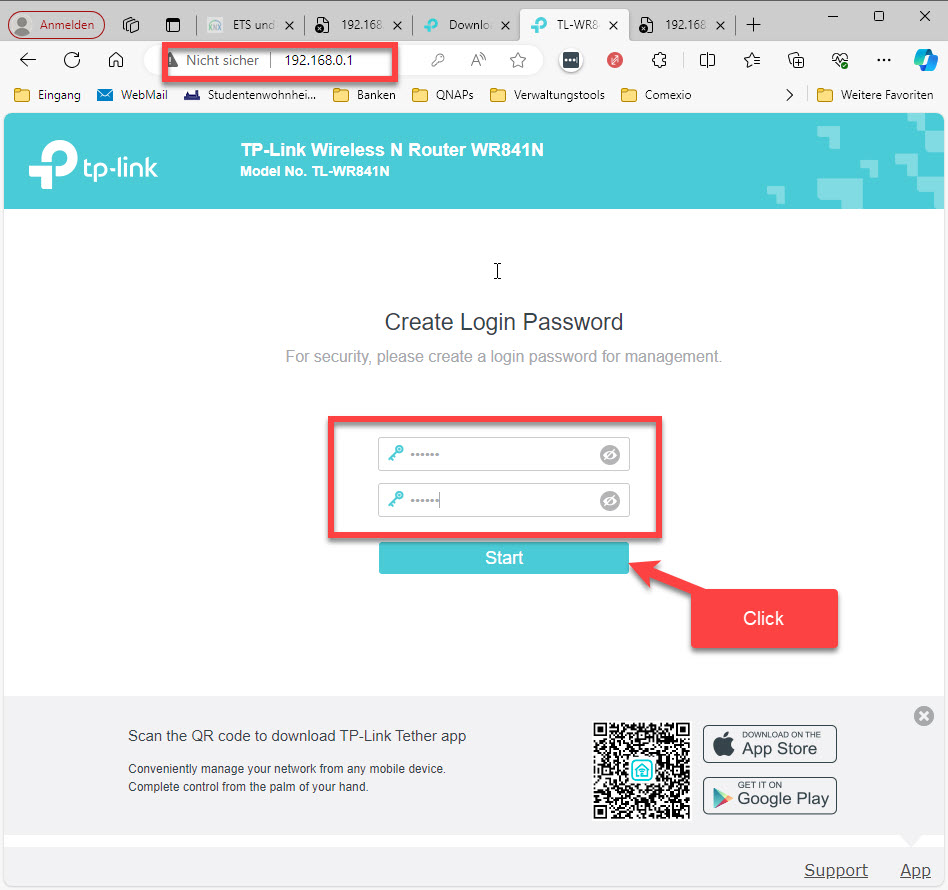
WLAN is not guaranteed there. That is why many students use a router (e.g. TP-Link TL-WR841N about 15€ or with fast WLAN6: TP-Link Archer AX10).
In houses that have LAN cable we do not guarantee WLAN – even if WLAN is often available.
In Clemensstrasse 127 some apartments are already connected to LAN cable – but we have good WLAN6 that works in every apartment.
If something does not work with the internet you need the following checklist, then you can call the internet hotline on 089-30623-1999.
-What is your VPN number
-Do you connect via CABLE or WLAN
-If via CABLE have you tried PPPoE? Is the cable in the correct socket
-What is the current IP address of the PC (169.X.X.X or 192.X.X.X or __________)
(How to find the IP address is explained further down this page or on Google for your device)
Without this information, help is not possible.
Own routers
In all apartments with a LAN connection you may run your own router.
But please note: Make sure you do not send DHCP services into our network!!!
Otherwise we have to hunt down the troublemaker at great effort. We charge a flat 100€ for that.
THEREFORE do not just plug it in. These devices must be configured!!!
Always plug the cable that leads into our network into the usually BLUE WAN port (Mikrotik "ETH1", TP-Link "WAN", FritzBox: set up first) – not!!! into the often YELLOW LAN port.
We have had good experience with MIKROTIK routers (e.g. Mikrotik RB941-2nD-TC at Reichelt.de for 19.90€ or
e.g. the better 5 GHz model RBD52G-5HacD2HnD-TC about 65 €).
Mikrotik routers are inexpensive, professional and from a European manufacturer.
Many students use routers from the Chinese manufacturer TP-Link – they are very cheap and easier for a one-time setup.
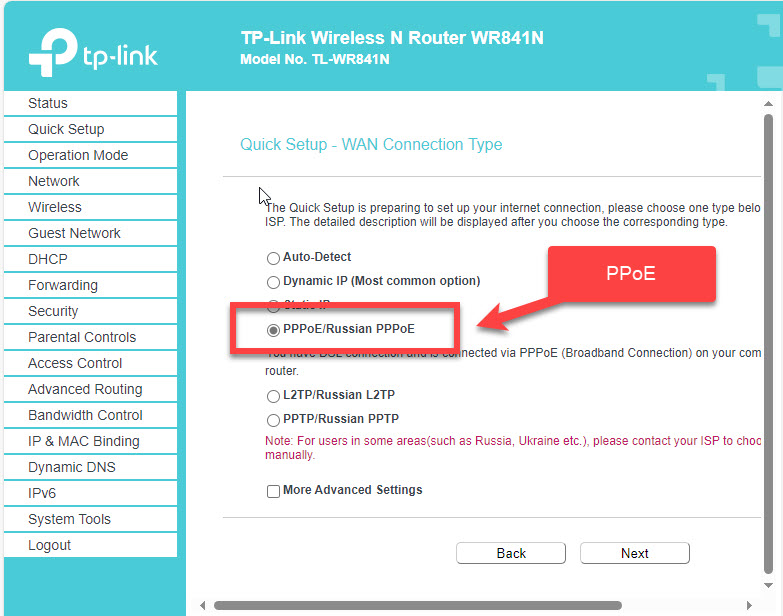
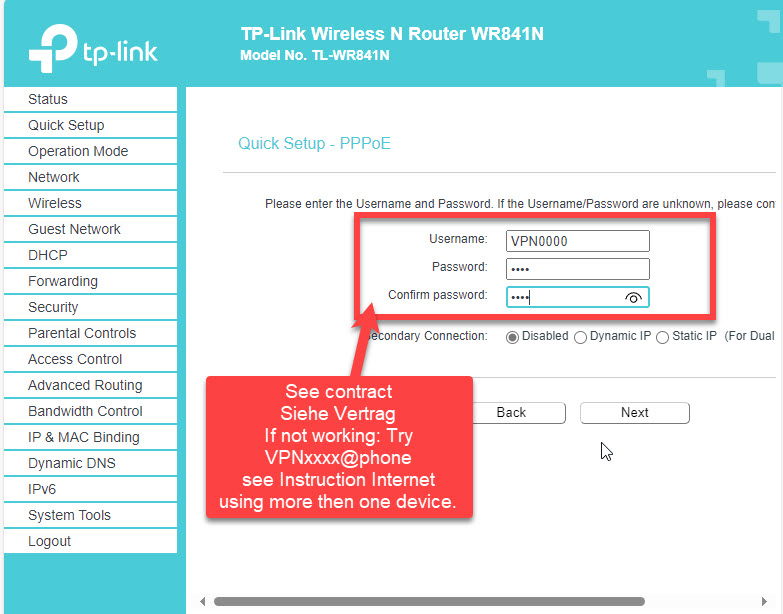
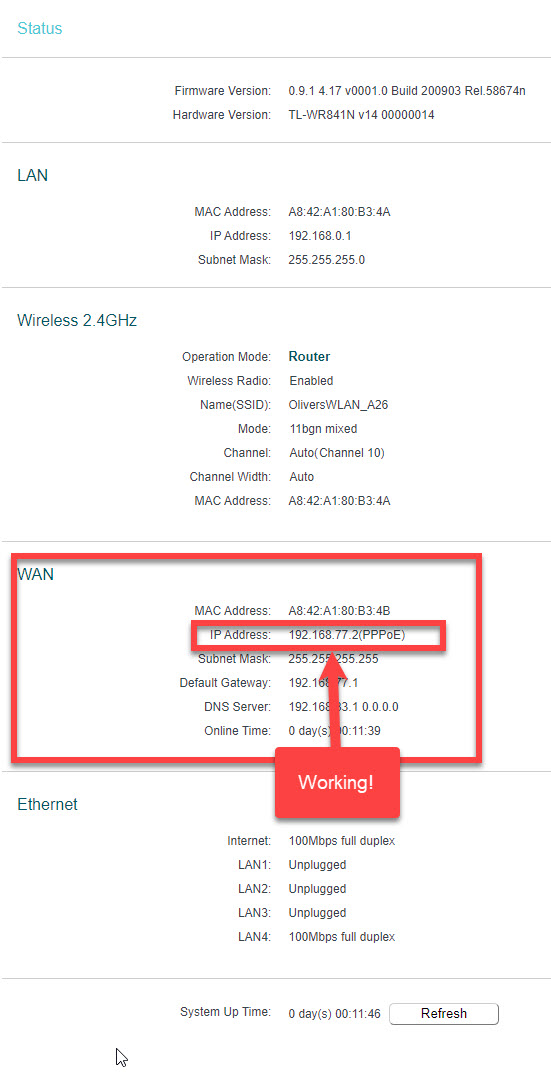
If you install a router, always use the PPPoE connection to our systems.
That is a professional, stable protocol and works without problems.
On Mikrotik a professionally set-up router looks like this: (Copy/Paste – change the login data yourself)
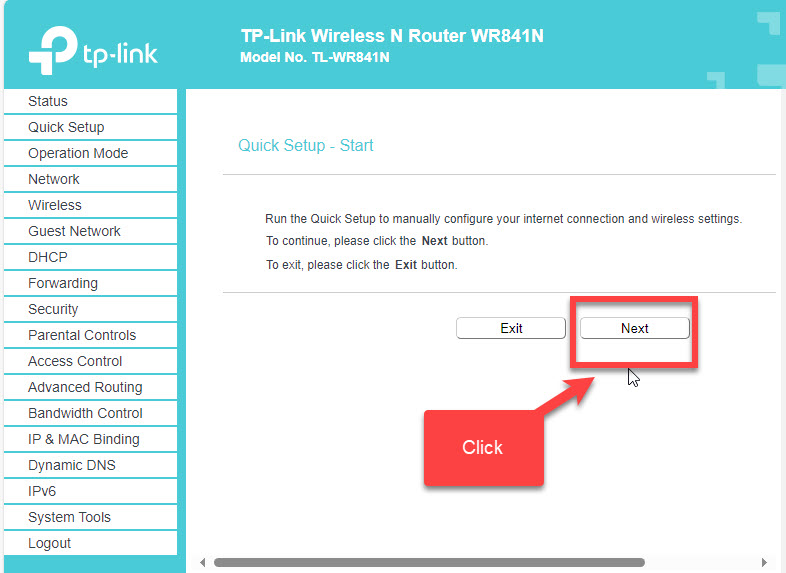
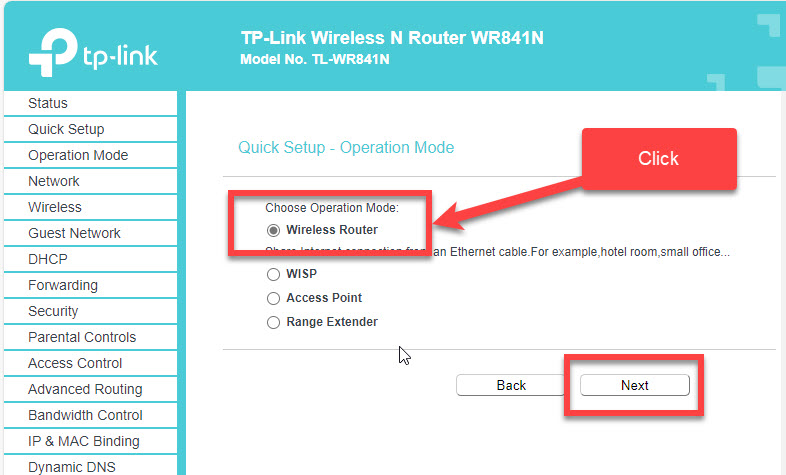
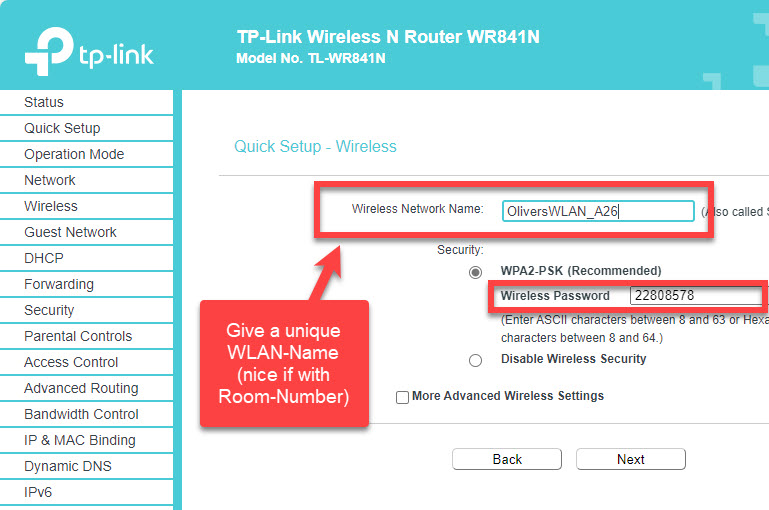
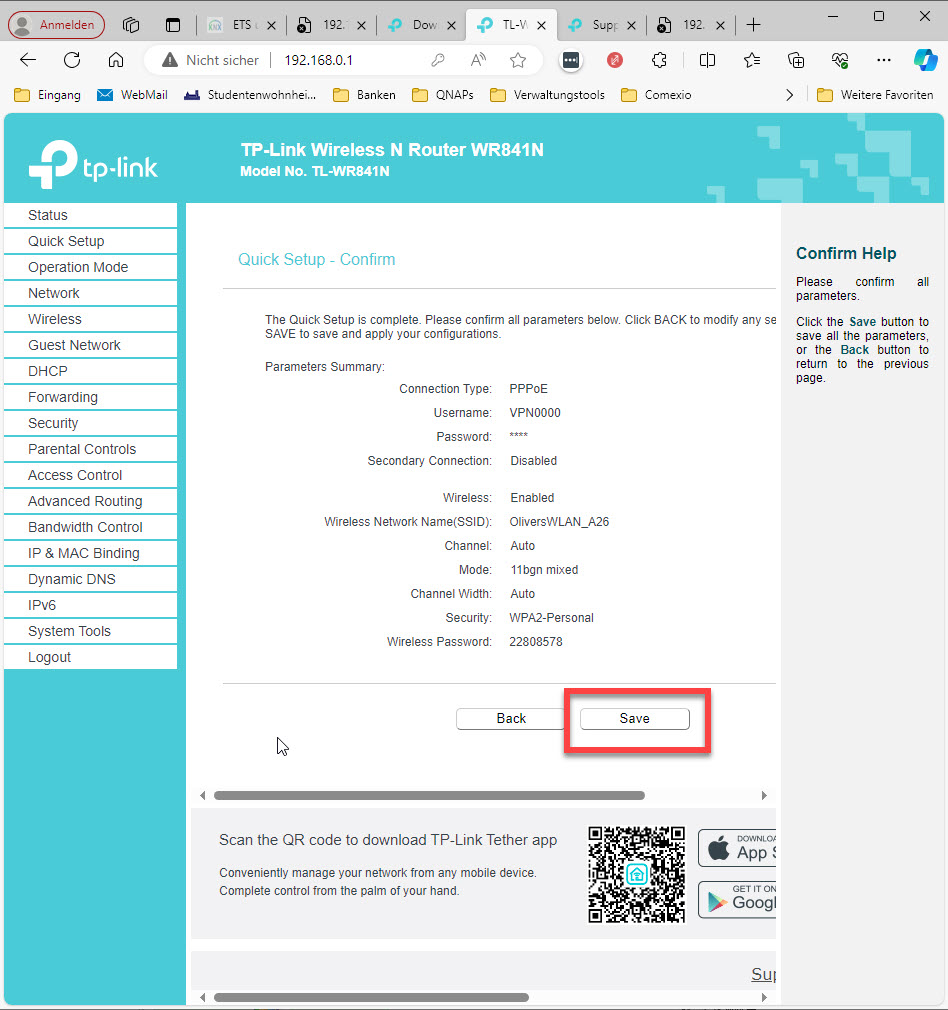
Example TP-Link
/interface bridge
add auto-mac=no comment=defconf name=bridge
/interface pppoe-client
add add-default-route=yes disabled=no interface=ether1 keepalive-timeout=60 \
name=Studentenwohnheim password=1234 use-peer-dns=yes user=1234@student
/interface wireless
set [ find default-name=wlan2 ] band=5ghz-a/n/ac channel-width=\
20/40/80mhz-XXXX distance=indoors frequency=auto installation=indoor \
mode=ap-bridge ssid=MikroTik-412924 station-roaming=enabled \
wireless-protocol=802.11
/interface list
add comment=defconf name=WAN
add comment=defconf name=LAN
/interface wireless security-profiles
set [ find default=yes ] authentication-types=wpa-psk,wpa2-psk eap-methods="" \
group-ciphers=tkip,aes-ccm mode=dynamic-keys supplicant-identity=MikroTik \
unicast-ciphers=tkip,aes-ccm wpa-pre-shared-key=passwort \
wpa2-pre-shared-key=passwort
add authentication-types=wpa-psk,wpa2-psk eap-methods="" \
management-protection=allowed mode=dynamic-keys name=profile1 \
supplicant-identity="" wpa-pre-shared-key=passwort \
wpa2-pre-shared-key=passwort
/interface wireless
set [ find default-name=wlan1 ] band=2ghz-onlyn channel-width=20/40mhz-XX \
country=germany disabled=no distance=indoors frequency=auto installation=\
indoor mode=ap-bridge security-profile=profile1 ssid=WLANZimmernummerAxx \
station-roaming=enabled wireless-protocol=802.11
/ip pool
add name=default-dhcp ranges=192.168.88.10-192.168.88.254
/ip dhcp-server
add address-pool=default-dhcp disabled=no interface=bridge lease-time=4w2d10m \
name=defconf
/interface bridge port
add bridge=bridge comment=defconf interface=ether2
add bridge=bridge comment=defconf interface=ether3
add bridge=bridge comment=defconf interface=ether4
add bridge=bridge comment=defconf interface=ether5
add bridge=bridge comment=defconf interface=wlan1
add bridge=bridge comment=defconf disabled=yes interface=wlan2
/ip neighbor discovery-settings
set discover-interface-list=LAN
/interface list member
add comment=defconf interface=bridge list=LAN
add comment=defconf interface=ether1 list=WAN
add interface=ether1 list=LAN
/interface wireless cap
set discovery-interfaces=ether1 enabled=yes interfaces=wlan2
/ip address
add address=192.168.88.1/24 comment=defconf interface=bridge network=\
192.168.88.0
/ip dhcp-client
add comment=defconf interface=ether1
/ip dhcp-server network
add address=192.168.88.0/24 comment=defconf gateway=192.168.88.1
/ip dns
set allow-remote-requests=yes
/ip dns static
add address=192.168.88.1 comment=defconf name=router.lan type=A
/ip firewall filter
add action=accept chain=input comment=\
"defconf: accept established,related,untracked" connection-state=\
established,related,untracked disabled=yes
add action=drop chain=input comment="defconf: drop invalid" connection-state=\
invalid disabled=yes
add action=accept chain=input comment="defconf: accept ICMP" disabled=yes \
protocol=icmp
add action=accept chain=input comment=\
"defconf: accept to local loopback (for CAPsMAN)" disabled=yes \
dst-address=127.0.0.1
add action=drop chain=input comment="defconf: drop all not coming from LAN" \
disabled=yes in-interface-list=!LAN
add action=accept chain=forward comment="defconf: accept in ipsec policy" \
disabled=yes ipsec-policy=in,ipsec
add action=accept chain=forward comment="defconf: accept out ipsec policy" \
disabled=yes ipsec-policy=out,ipsec
add action=fasttrack-connection chain=forward comment="defconf: fasttrack" \
connection-state=established,related disabled=yes
add action=accept chain=forward comment=\
"defconf: accept established,related, untracked" connection-state=\
established,related,untracked disabled=yes
add action=drop chain=forward comment="defconf: drop invalid" \
connection-state=invalid disabled=yes
add action=drop chain=forward comment=\
"defconf: drop all from WAN not DSTNATed" connection-nat-state=!dstnat \
connection-state=new disabled=yes in-interface-list=WAN
/ip firewall nat
add action=masquerade chain=srcnat comment="masquerade network" \
ipsec-policy=out,none out-interface-list=WAN
add action=masquerade chain=srcnat comment="defconf: masquerade" \
ipsec-policy=out,none out-interface=Studentenwohnheim
/snmp
set enabled=yes
/system clock
set time-zone-name=Europe/Berlin
/system identity
set name="Zimmernummer Privat"
Picture of how a Mikrotik router is set up, for example